An automation worked yesterday and now its API call returns 401. The temptation is to rebuild the node, regenerate every credential, or add retries. Start by identifying what changed and which service is rejecting the request.
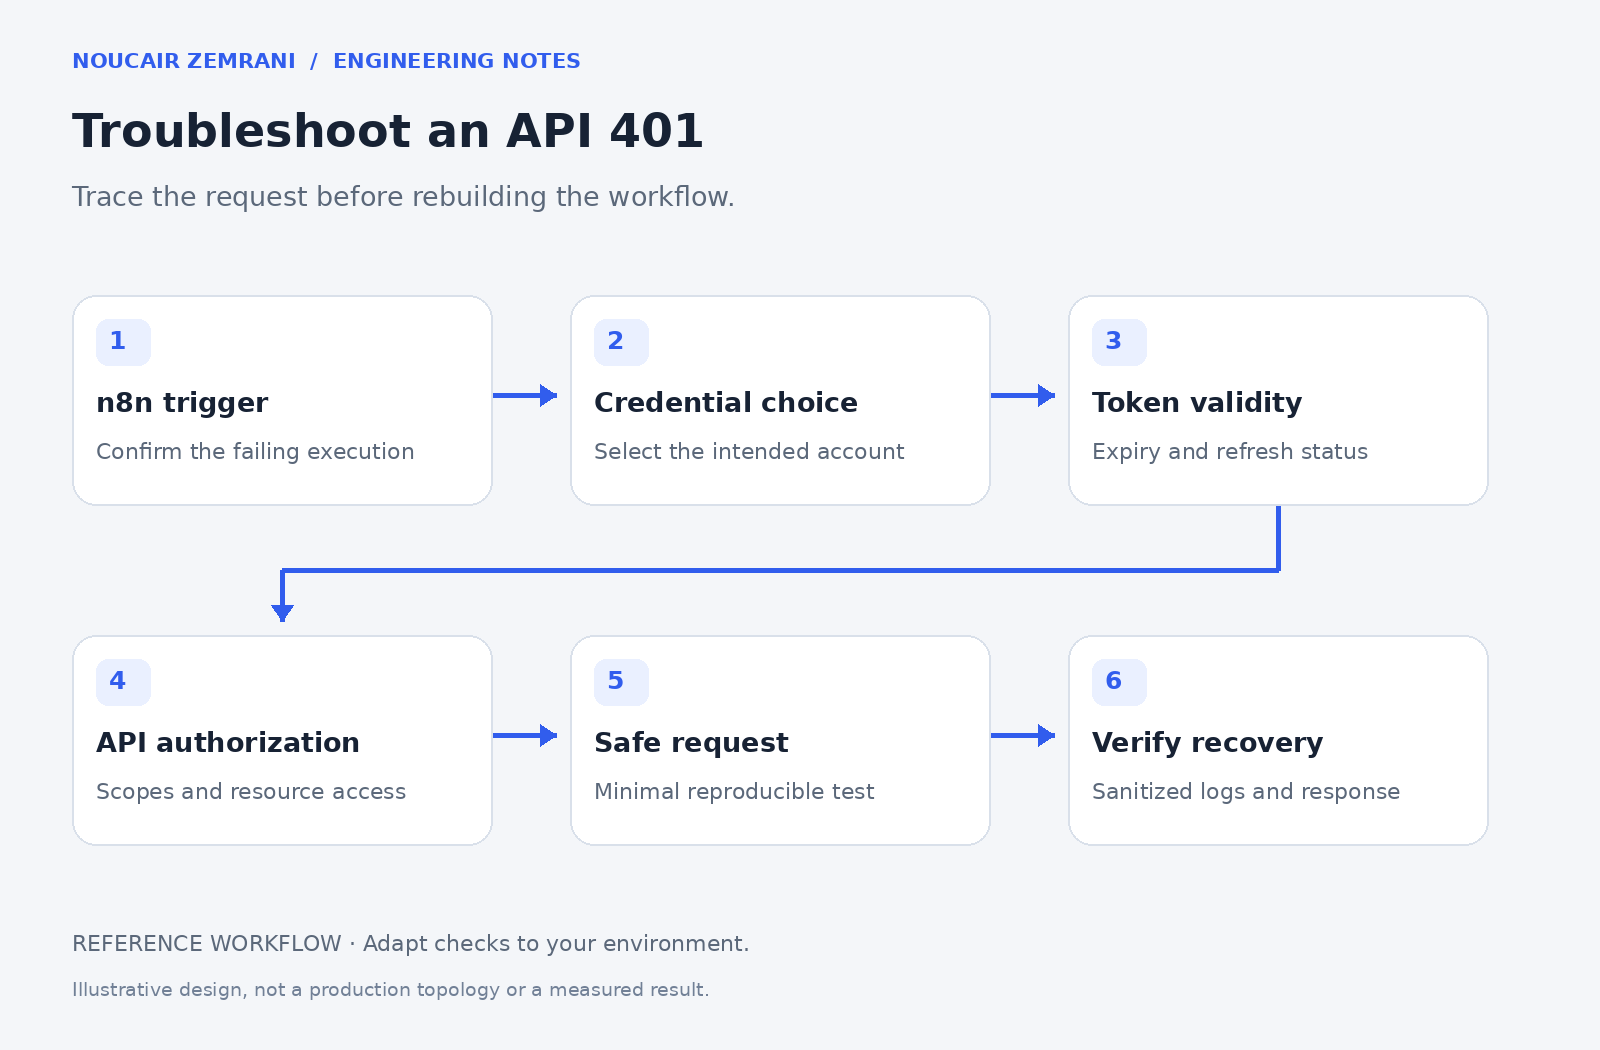
My automation work includes n8n, webhooks, REST APIs, and WhatsApp integrations. Authentication failures are best treated as a diagnosis task with evidence, rather than as a reason to rebuild the entire workflow.
Capture the smallest useful evidence
Record the failing node, execution time, HTTP method, destination service, response status, and sanitized error message. Preserve a provider request identifier when available. Never paste bearer tokens, passwords, or real customer payloads into public screenshots or support posts.
Compare the failing execution with the most recent successful one. Did the endpoint, environment, credential selection, account, or authentication method change? A workflow may be using a test credential against a production resource even though each item looks valid in isolation.
Check credential validity and authorization separately
Confirm whether the credential is expired, revoked, rotated, or associated with the wrong account. Check the provider’s required scopes and resource permissions. APIs differ in how they report authentication and permission problems, so read the response body and provider documentation instead of inferring everything from the status number alone.
For OAuth integrations, verify the supported refresh flow and credential configuration. For static tokens, identify who owns renewal and where expiry is tracked. Replacing a token without addressing the lifecycle leaves the same failure waiting to return.
Verify without repeating the business action
Use a harmless read operation or an isolated test resource when the API supports it. Keep the test close to the failing request so it checks the same account and permission path. Avoid rerunning an entire workflow that could send messages, create orders, or generate duplicate documents.
Once authentication works, resume processing deliberately. Decide whether previous failed items need replay and whether any earlier steps already completed. Successful authentication does not make the rest of an execution automatically safe to repeat.
Leave a useful handover
Record the cause, the credential owner, the expiry or refresh behavior, the recovery procedure, and an alert path. A simple runbook should let another person distinguish credential expiry from a network outage or invalid payload.
If one workflow has stopped at an API call, send a sanitized error and a description of the expected outcome. I can help scope a diagnosis, tested fix, and practical handover.